Aranis turns your tools, audits and vendor questionnaires into situational awareness of risk.
Built on recognized frameworks
Modules
No module matters more than another. Turn on what you need and centralize all your risk intelligence in one place.
Inside the platform


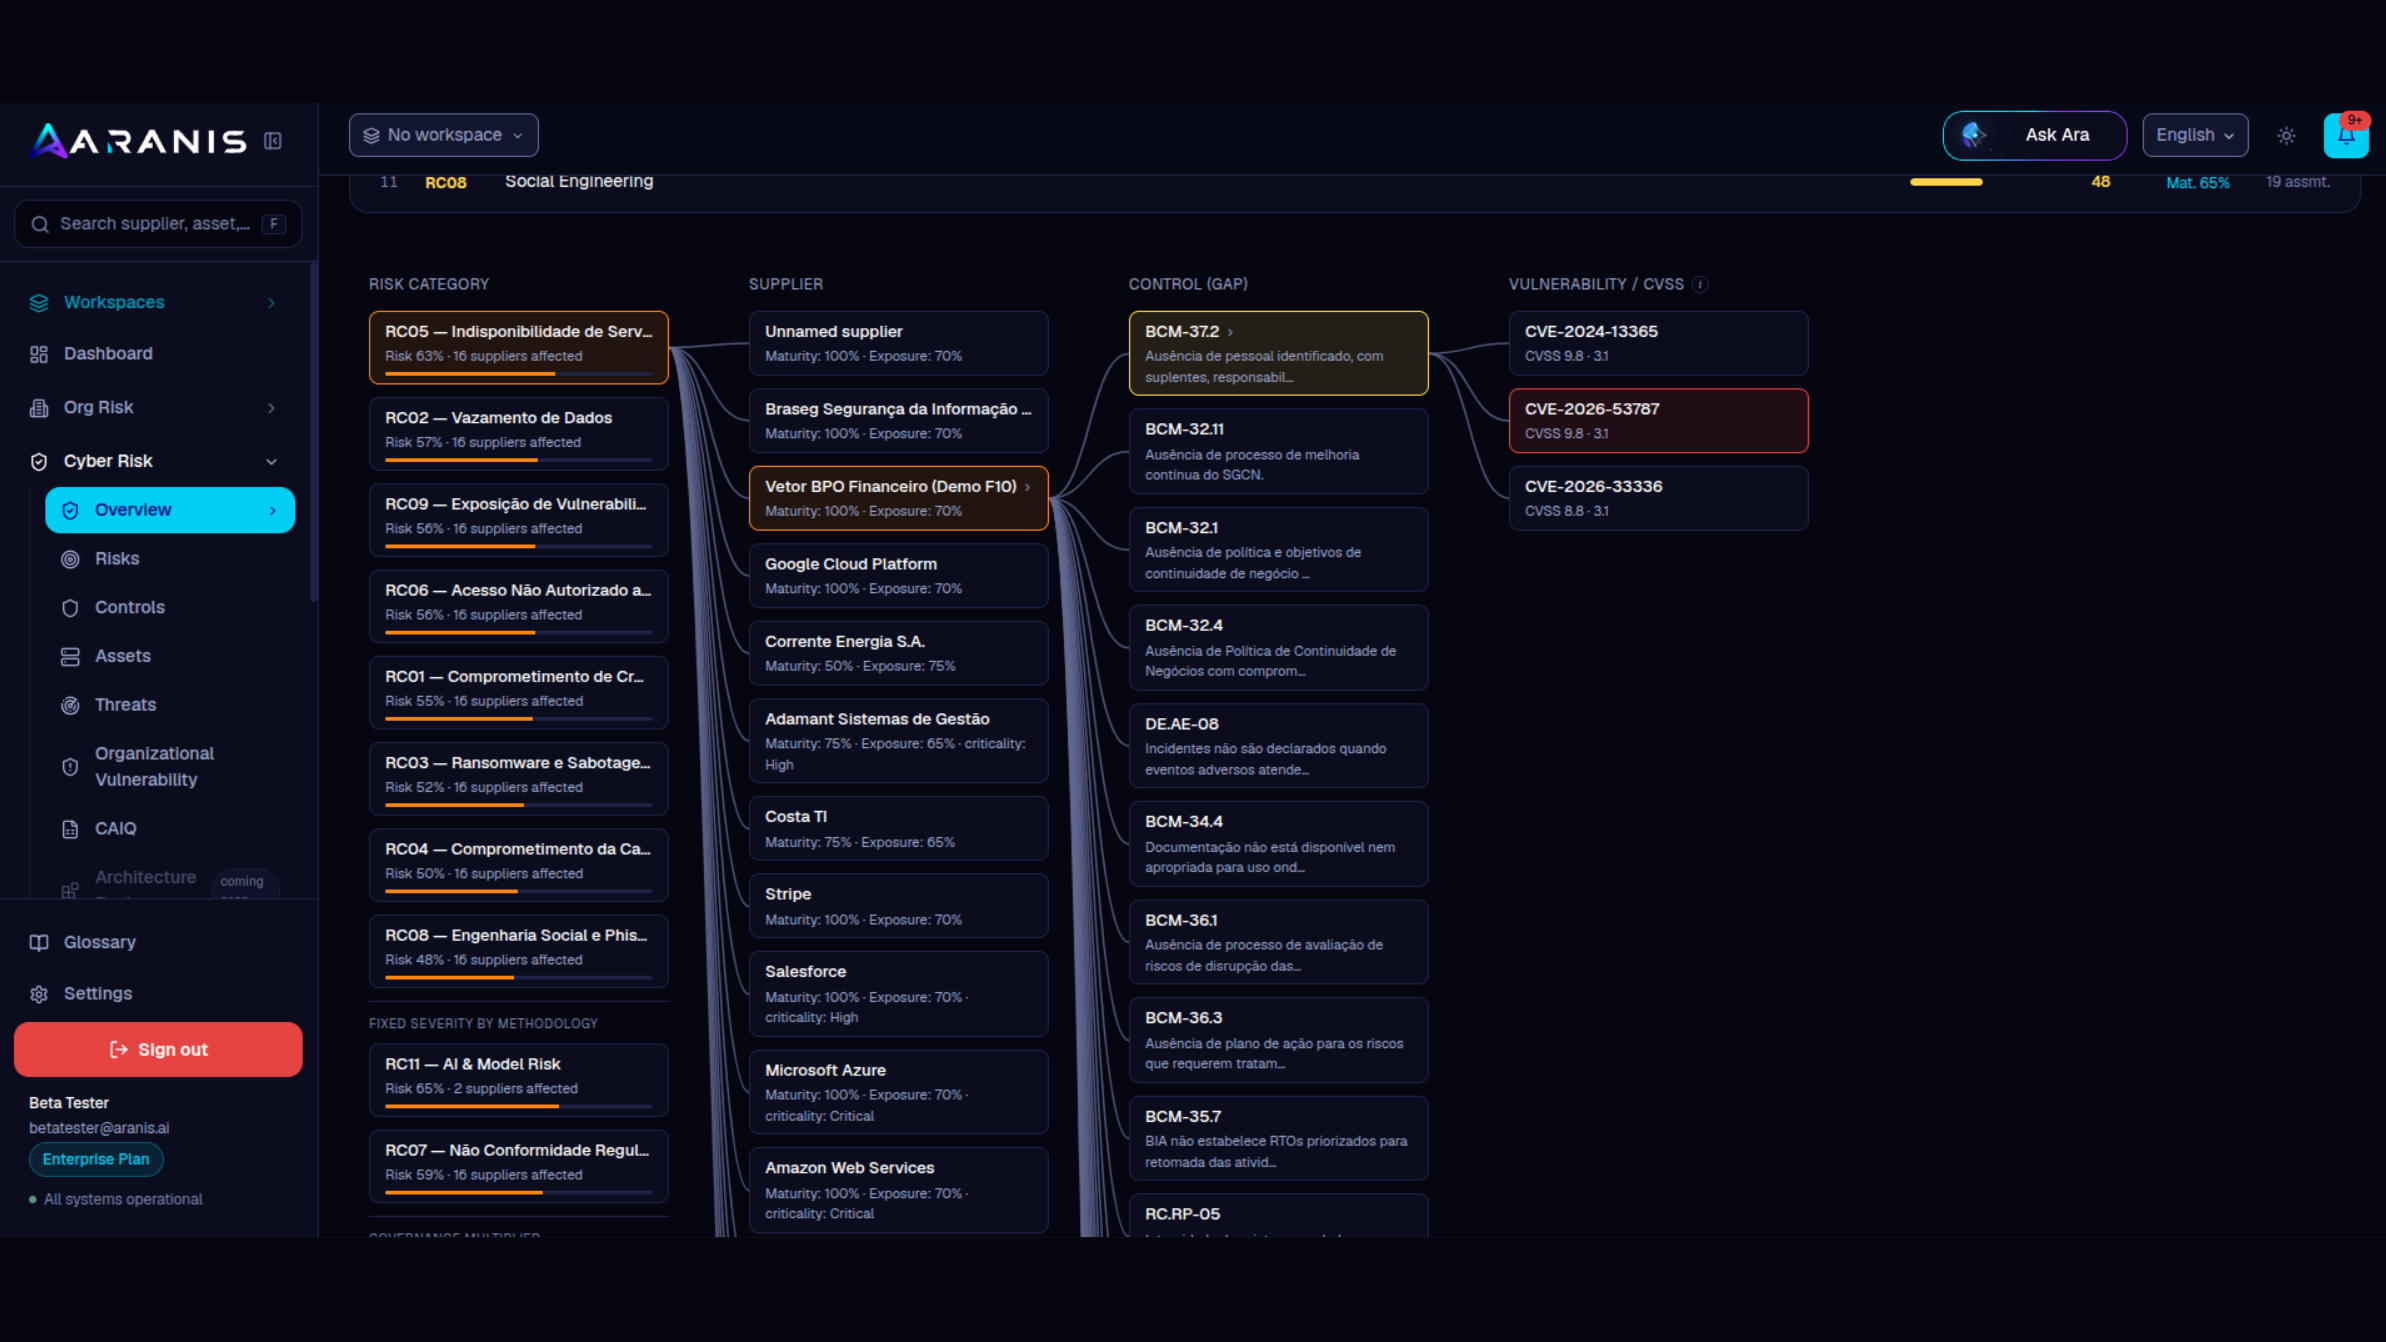
Risk Path links the risk category to the vendor, to the control with a gap, and to the MITRE ATT&CK technique that gap enables. Not a score — the path an attack would take.

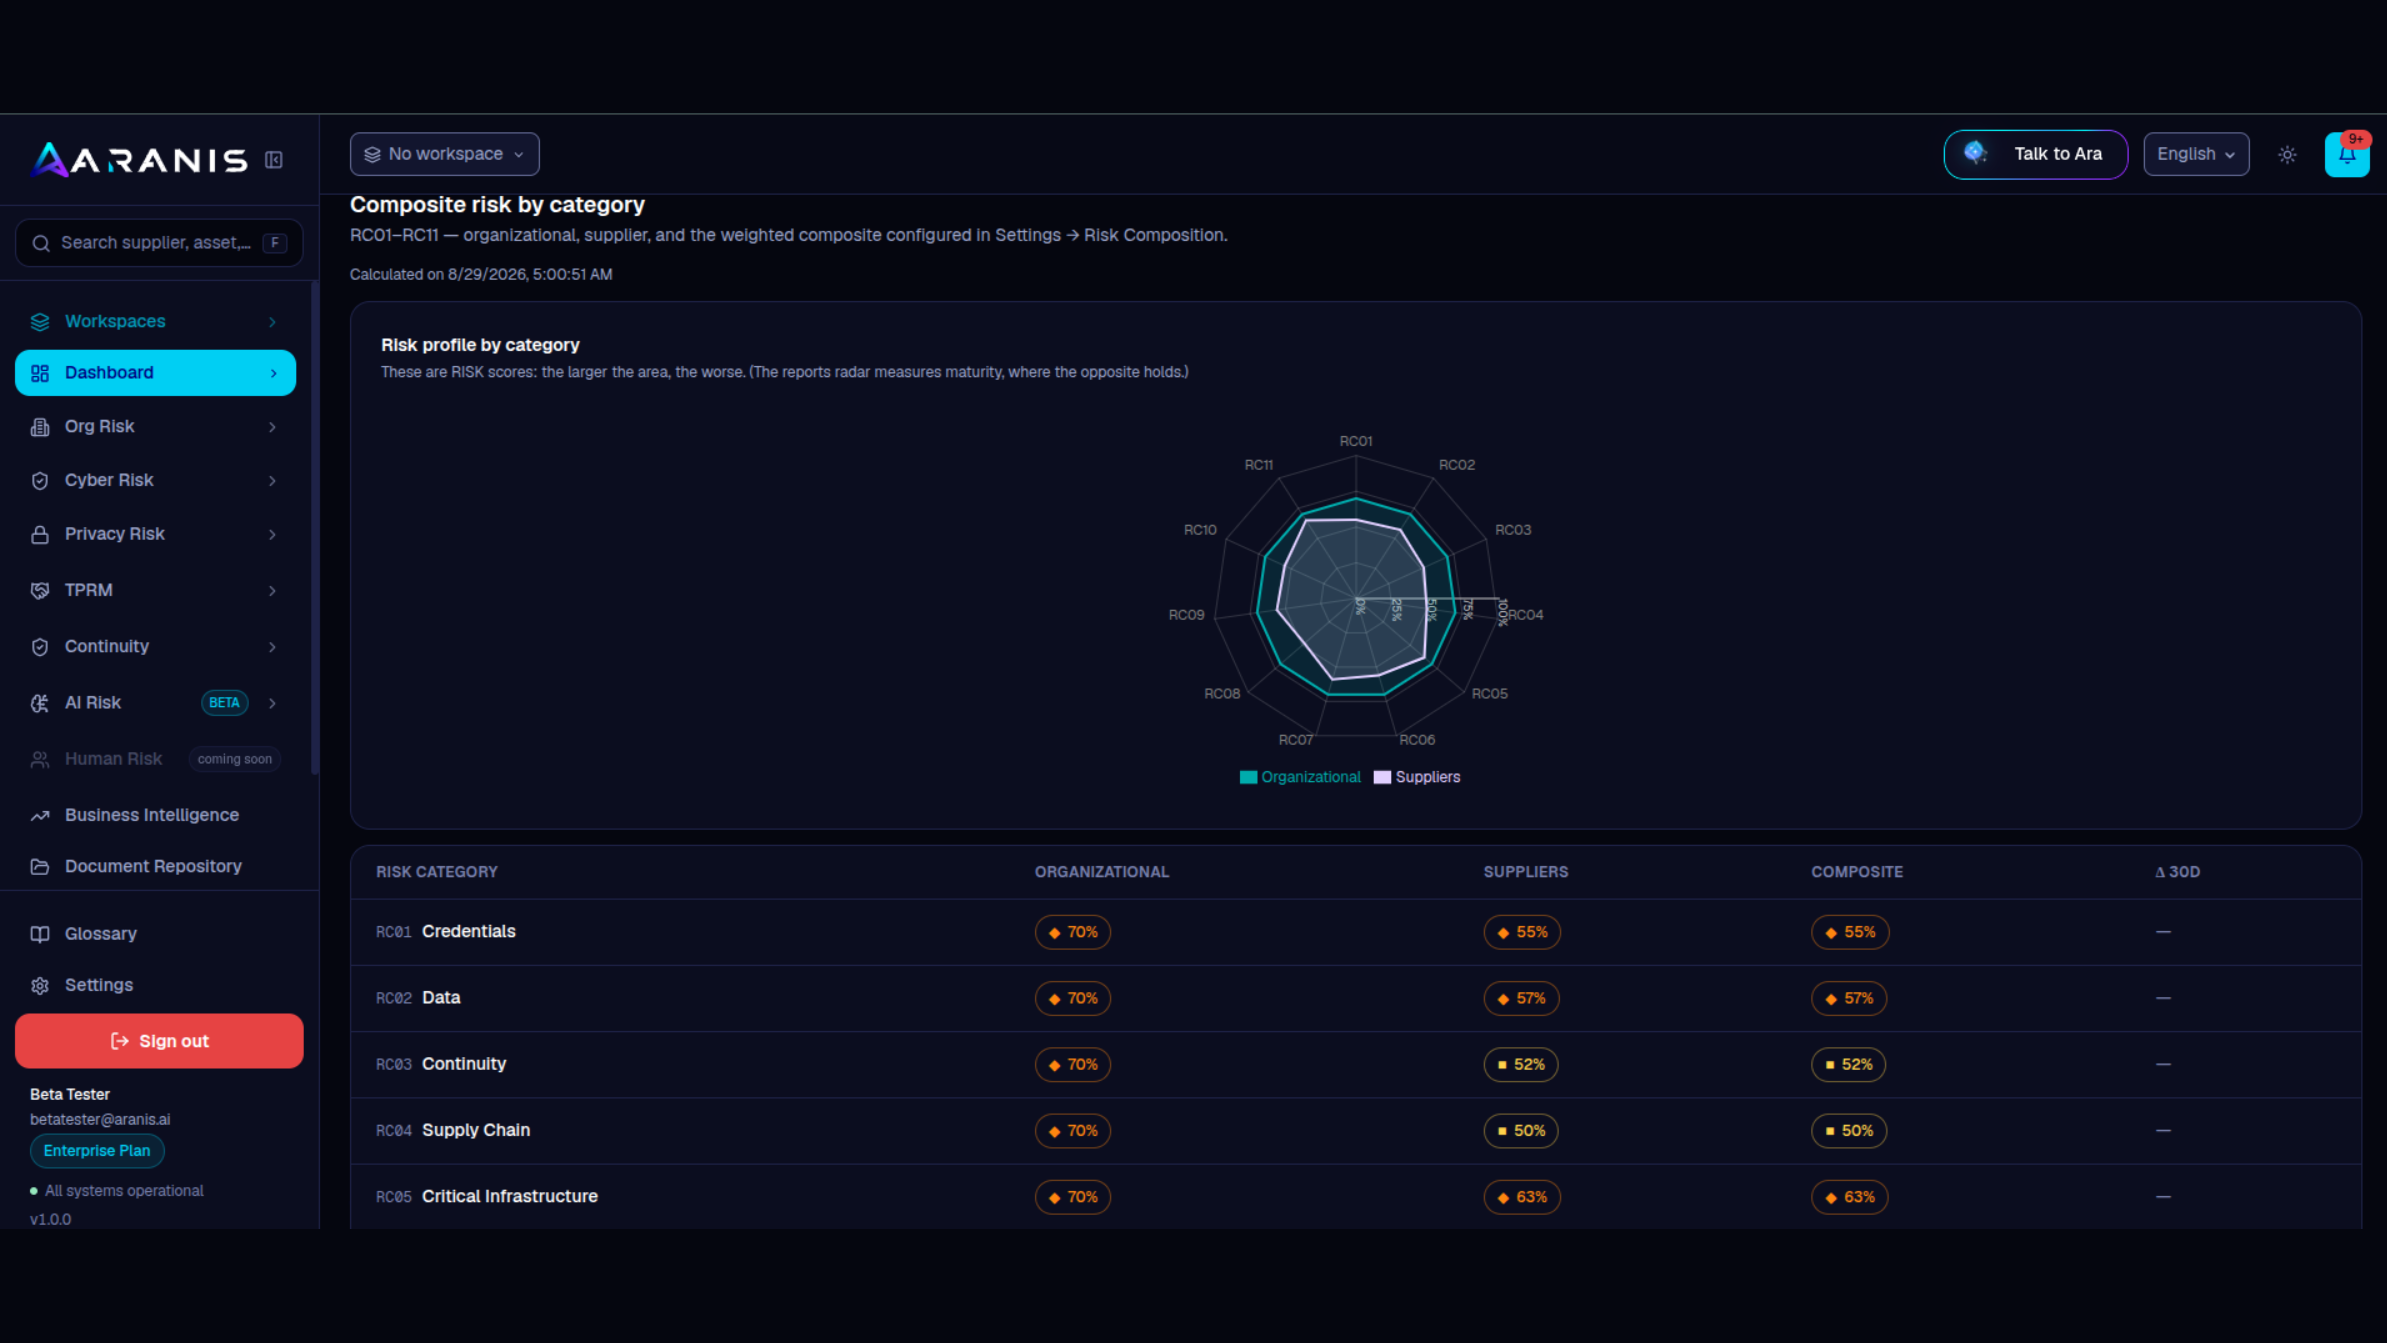
The composite score weighs your own self-assessment against the aggregate risk of your vendor portfolio, category by category. Neither number alone says where you stand.

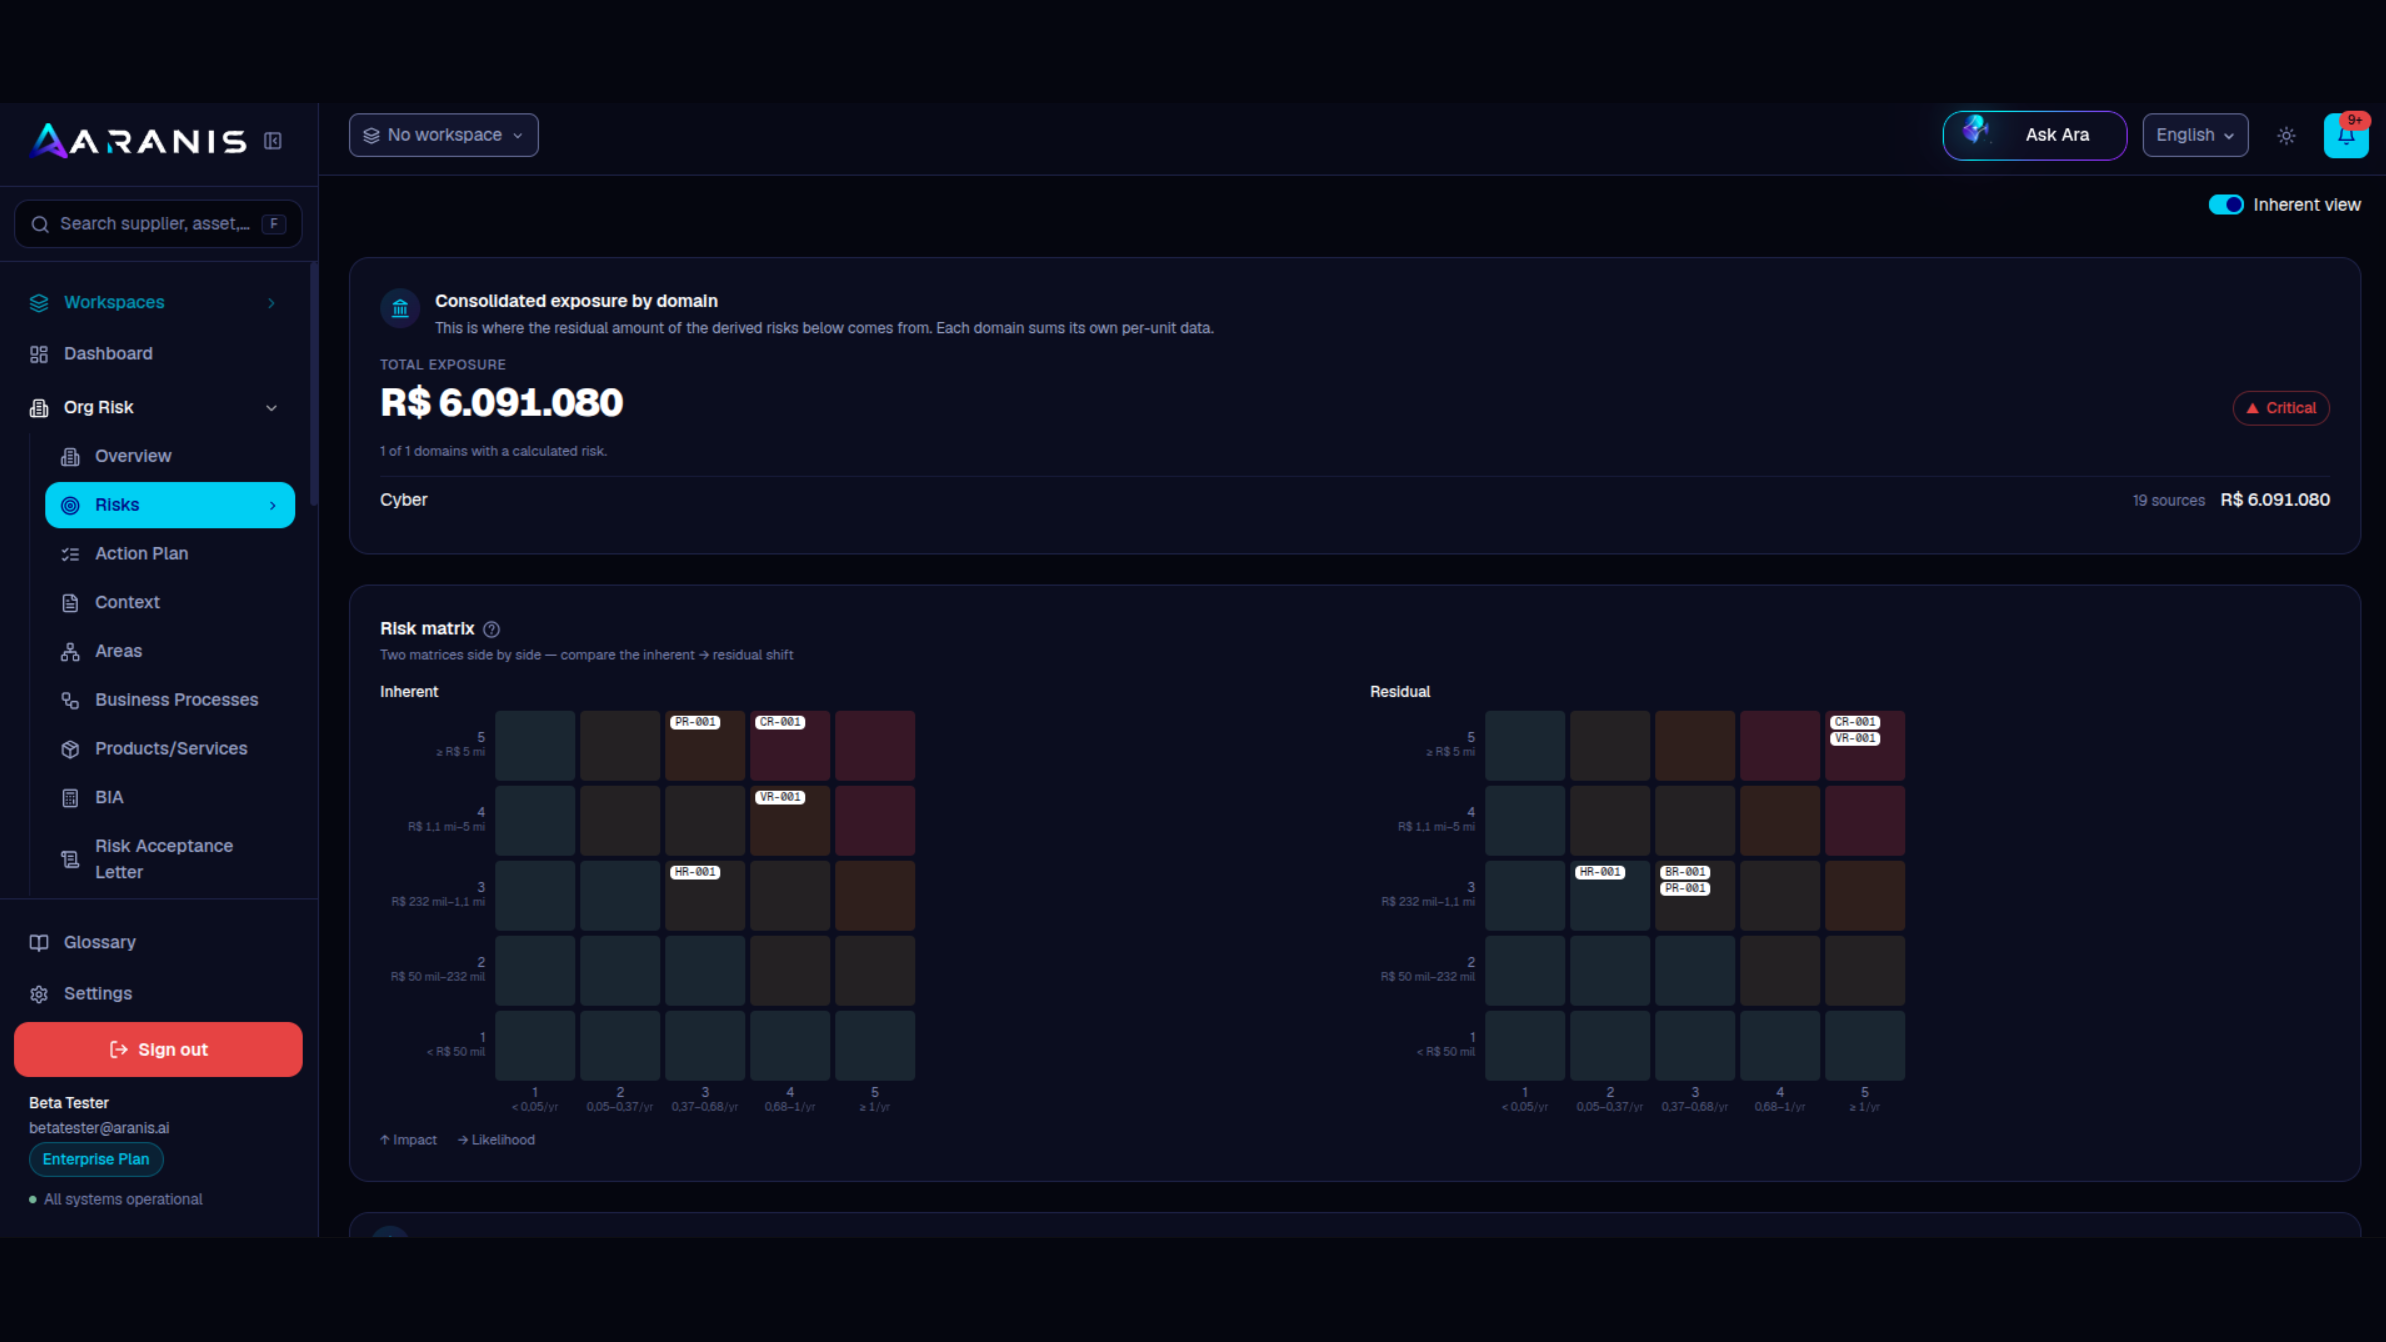
What the audit records as non-compliant becomes financial exposure on the board’s screen. And what has not been measured yet shows as unmeasured — never as zero.

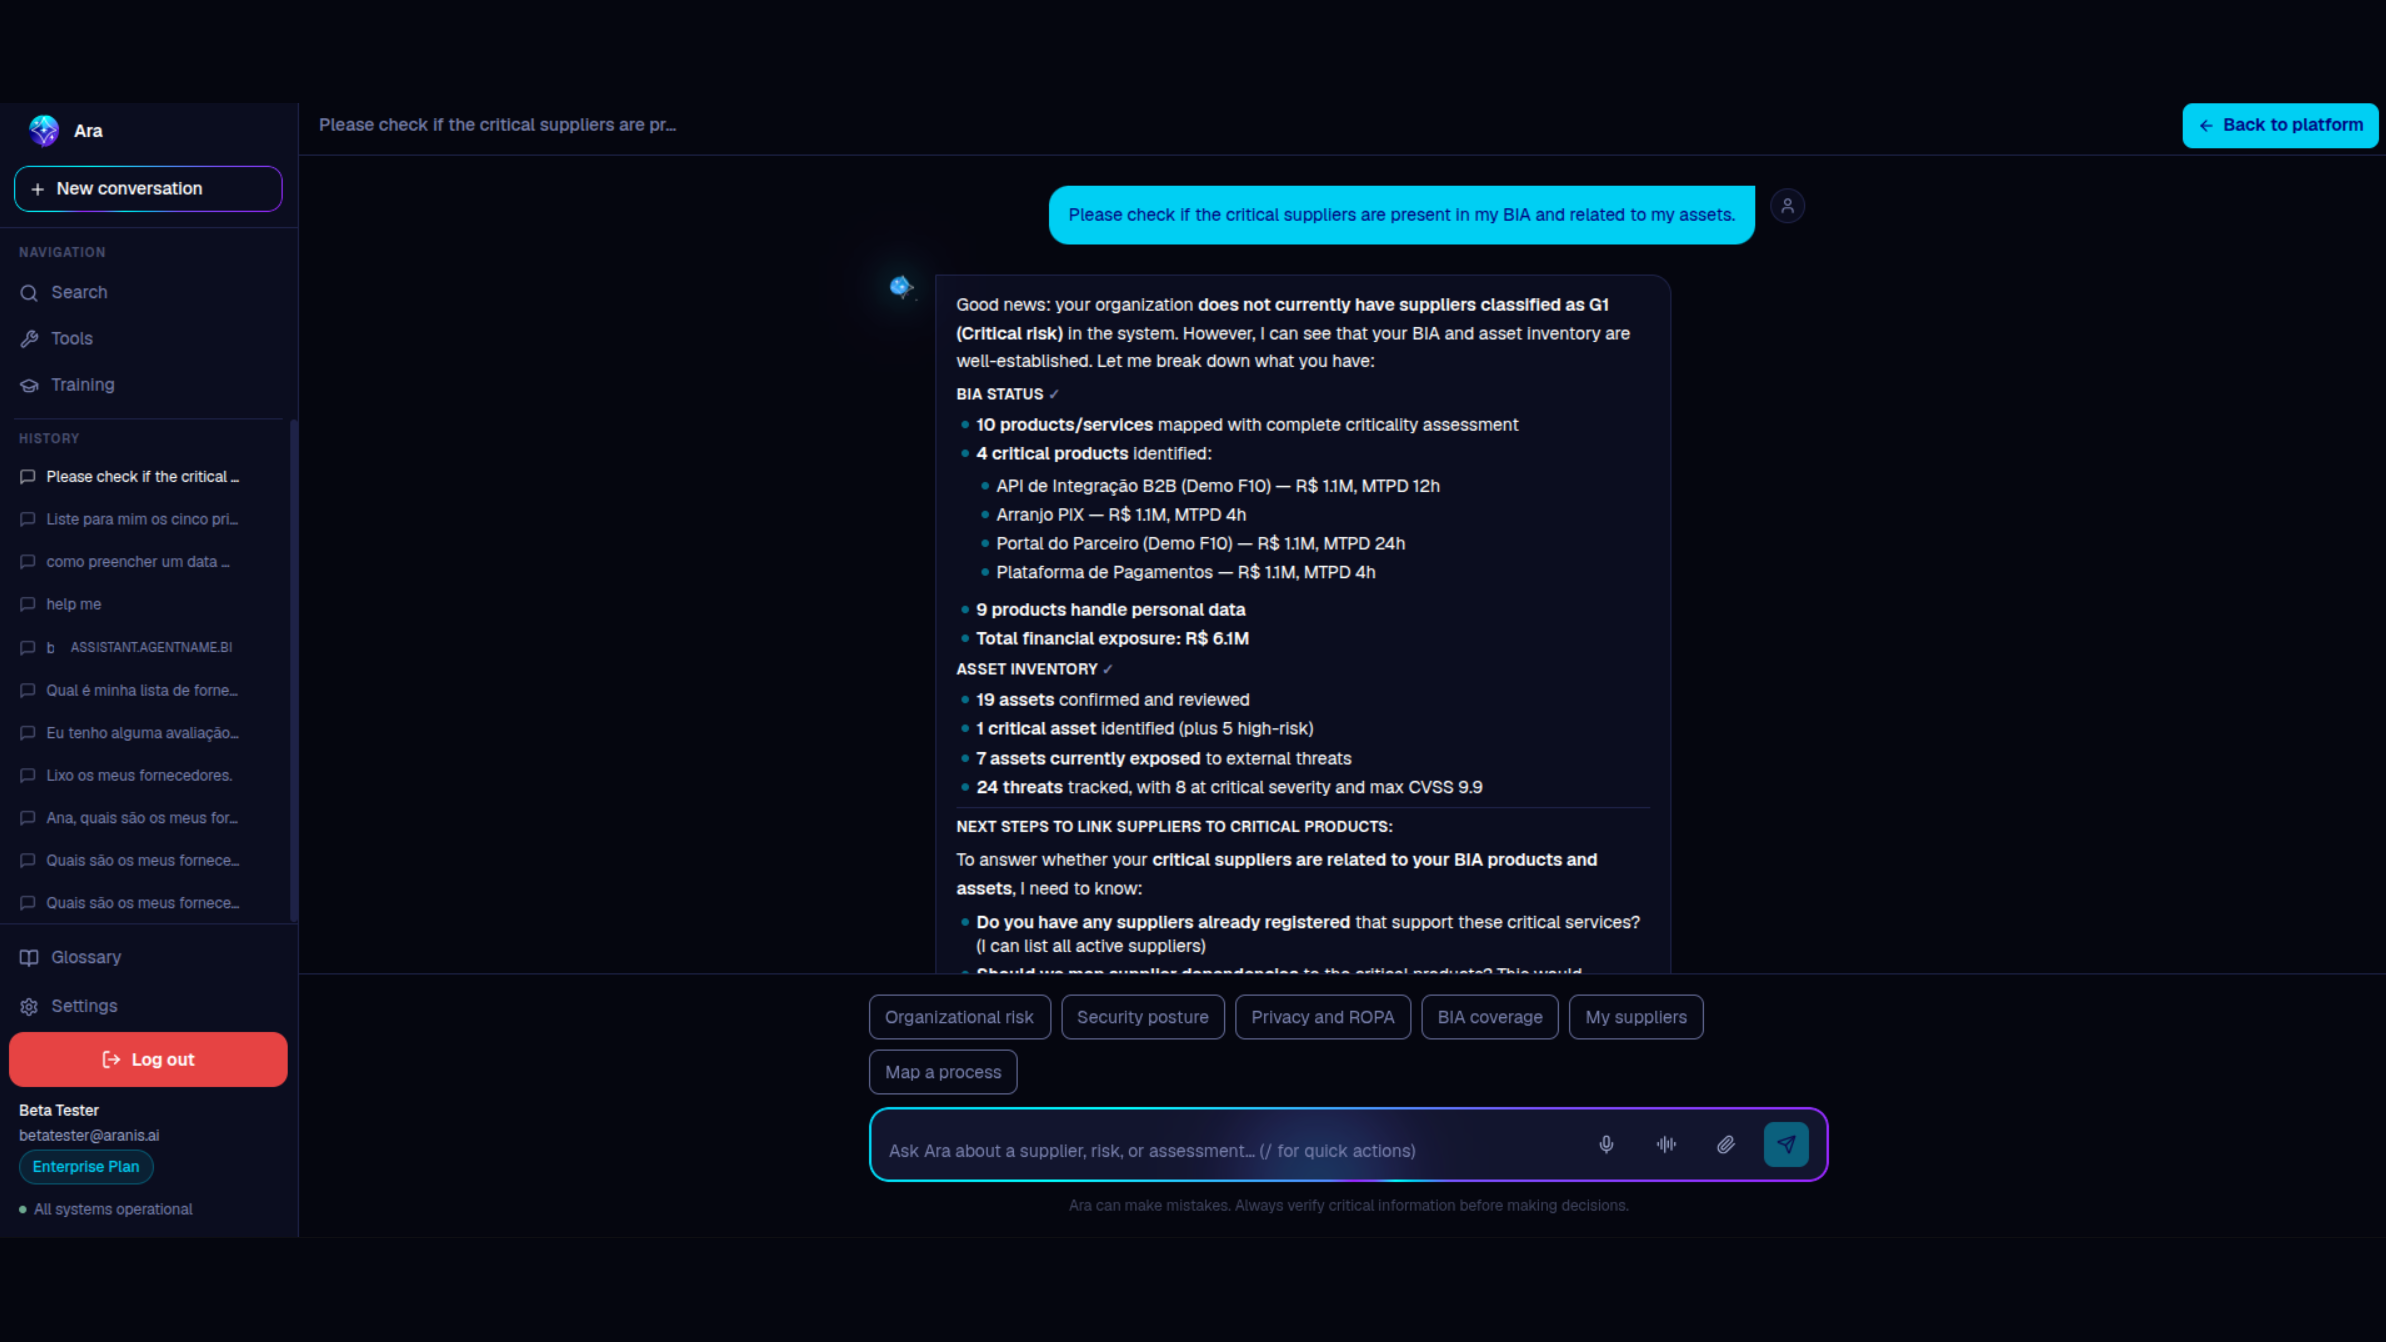
Ask in plain language and Ara answers with context from vendors, assessments, controls, action plans, BIA and privacy — without you changing screens to assemble the pieces.
The problem
Every team has its own score: the vendor, the exposed domain, the critical process, the personal-data inventory. Nobody has the sum — and the sum is what decides.
The vendor gap, the domain exposure and the critical process were all on record. In three systems that do not talk to each other — which is why nobody connected them in time.
The auditor signs the control off on paper. The incident does not ask the auditor — it asks whether the control was working that day, and the answer has to be on record.
How it works
See it in action
A walk through the platform: the dashboard with consolidated organizational risk, privacy coverage, the Data Map with where each piece of data comes from and goes, the LGPD Canvas, and Ara answering by voice.
Features
Technical validation
Aranis' 257 controls were derived from the consolidation of four internationally recognized frameworks, adapted to the Brazilian regulatory landscape.
NIST CSF 2.0
Cybersecurity Framework
View coverage →LGPD
Lei Geral de Proteção de Dados
View coverage →GDPR
EU Data Privacy
View coverage →SOC 2
Audit & Compliance
View coverage →ISO 22301
Business Continuity
View coverage →NIST AI RMF
AI Risk Management
View coverage →NIST CSF 2.0
Cybersecurity Framework
View coverage →LGPD
Lei Geral de Proteção de Dados
View coverage →GDPR
EU Data Privacy
View coverage →SOC 2
Audit & Compliance
View coverage →ISO 22301
Business Continuity
View coverage →NIST AI RMF
AI Risk Management
View coverage →Pricing
Every plan includes the risk modules, Ara and audit-ready evidence. What changes is the volume.
To start on your own, no card.
Get started
Create your account and start centralizing your business's risk intelligence in minutes.